Catch firewalls running old threat content
Every night, WebRun signs in to your Palo Alto Networks management console, reads the content update and software version on every firewall and device group, compares each against the newest version available, checks subscription status, posts the devices that are behind to Slack, and cards the laggards in Trello.
- No credit card
- Under $0.01 per run
- Cancel anytime
How do I check which firewalls are behind on threat content updates?
WebRun signs in to your Palo Alto Networks console every night and reads the content update and software version on each managed firewall, along with its subscription status. It posts the devices sitting behind the newest version to Slack and cards each laggard in Trello for the network team.
- Devices behind on threat content surface the same night
- Lapsed subscriptions are called out separately, not buried
- The run is read-only: no update is installed without a human
Built for network security engineers · security operations teams · IT infrastructure teams · managed service providers
What does WebRun do on every run?
The exact actions WebRun takes, in order - in plain language, so you can adjust anything.
-
WebRun signs in and gets to work
Opens
www.paloaltonetworks.comin a real browser with your saved login - no setup, no API keys. -
1
Palo Alto Networks - read versions per device
paloaltonetworks.com
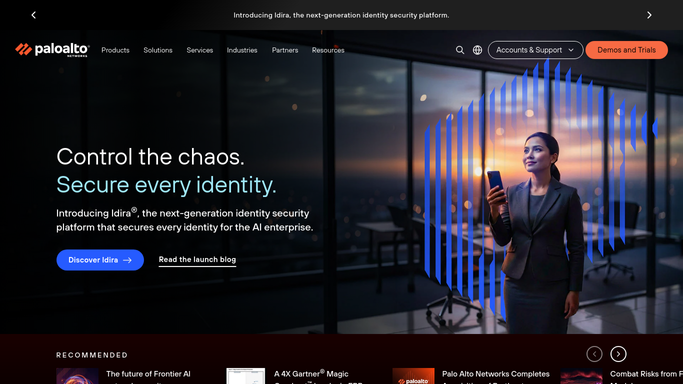
WebRun opens Palo Alto Networks to read versions per device. - Sign in to your Palo Alto Networks management console and list the managed firewalls
- For each device, read the installed content update version and the software version
- Read the newest content version available and work out how far behind each device sits
- Check the subscription and licence status on each device and flag anything lapsed or close to lapsing
- Group results by device group so the pattern is easy to see
Done when Every firewall has its content version, software version, and subscription status recorded.
-
2
Slack - post the devices behind
slack.com How to Automate Slack

WebRun opens Slack to post the devices behind. - Post tonight's coverage summary to your network security channel in Slack
- List only the devices behind the newest content version, with how far behind each is
- Call out any lapsed subscription separately, since that stops updates entirely
- Say plainly when the whole estate is current so the team knows the check ran
Done when The security channel knows which firewalls are behind tonight.
-
3
Trello - card each laggard device
trello.com How to Automate Trello
WebRun opens Trello to card each laggard device. - Open your network operations board in Trello
- Add a card per device that is behind, naming the device group and the version gap
- Put devices with a lapsed subscription at the top since they receive nothing new
- Close cards for devices brought current since the last run
Done when Every device needing an update has a card on the board.
How is each run configured?
Secure by default
Connect once, stays signed in
WebRun signs in once and keeps each session in a persistent environment, so every run picks up right where it left off.
Every action is checked against this policy before it runs.
Questions, answered
Will it install an update or reboot a firewall?
No. WebRun reads versions and reports the gaps. Installing content, upgrading software, or rebooting a device stays a change-controlled human action.
Does it change any firewall policy?
No. This run is read-only. WebRun does not create, edit, or push a policy rule, and it does not commit any configuration change.
What about devices that are already current?
They are left out of the Slack post and the board. WebRun confirms in one line that the estate is current so silence never means the check failed.
Related templates
Put this on autopilot.
Turn it on in minutes - or have our team set it up for you.